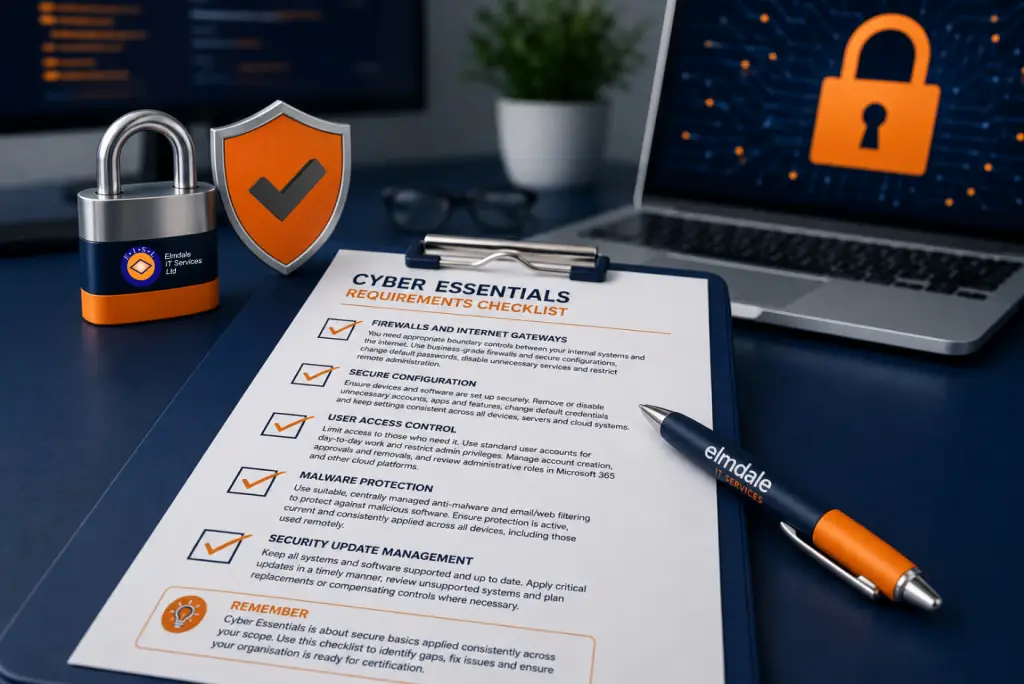
If you are planning for certification, a clear cyber essentials requirements checklist can save a great deal of wasted time. Many organisations assume Cyber Essentials is mainly a paperwork exercise, then find the real challenge is proving that day-to-day security basics are actually in place across users, devices and systems.
That is why preparation matters. For small and mid-sized businesses, schools and multi-site organisations, the scheme is usually very achievable, but only if you look beyond the questionnaire and check how your environment works in practice. The standard is designed to assess a defined set of technical controls, and small oversights such as an unused admin account, an unsupported laptop or inconsistent update settings can hold things up.
What the Cyber Essentials requirements checklist is really for
A good checklist is not just a list of boxes to tick. It helps you confirm whether your organisation is meeting the five core control areas expected under Cyber Essentials and whether those controls apply consistently across your scope.
That last point matters. Certification is based on the systems, users and devices within the scope you declare. If your organisation has a simple single-office setup, that may be straightforward. If you have remote workers, cloud services, school devices, guest networks or a mix of old and new systems, you need to be more deliberate. The checklist should help you define what is included, identify weak spots and fix them before assessment.
Cyber Essentials requirements checklist: the core areas
Firewalls and internet gateways
You need appropriate boundary controls between your internal systems and the internet. In practice, that usually means business-grade firewall protection, secure router configuration and clear rules about what traffic is allowed in and out.
The common problem here is assuming the default setup is enough. It may be, but only if it has been reviewed properly. Default passwords must be changed, unnecessary services should be disabled, and management interfaces should not be exposed carelessly to the internet. If remote administration is needed, it should be restricted and protected.
For smaller organisations using broadband routers, this is often the first area that benefits from expert review. What looks functional is not always aligned with the standard.
Secure configuration
Cyber Essentials expects devices and software to be set up securely. That includes removing or disabling unnecessary accounts, apps and features, changing default credentials, and making sure users are not routinely given more access than they need.
This is where many organisations discover drift. Over time, extra software gets installed, old user accounts remain active, and laptops are deployed with different settings depending on who set them up. A secure configuration standard helps bring consistency back.
It is also worth checking mobile devices, servers and cloud-administered systems, not just office PCs. If they are in scope, they need the same attention.
User access control
Access should be limited to the people who need it, and administrative privileges should be tightly controlled. Staff should generally use standard user accounts for everyday work, with separate admin accounts where elevated rights are genuinely required.
This sounds simple, but it is one of the most frequent stumbling blocks. In many organisations, a handful of users have local admin rights because it was convenient at the time. That may solve a short-term software issue, but it increases risk significantly.
Your checklist should cover how new accounts are created, how leavers are removed, how privilege is approved, and whether dormant accounts still exist. If you use Microsoft 365 or other cloud platforms, include those admin roles too. Cyber Essentials does not stop at the office server cupboard.
Malware protection
You need suitable protection against malicious software. For most organisations, that means centrally managed anti-malware tools, sensible filtering and controls that reduce the chance of unsafe files being run in the first place.
There is some flexibility in how this is achieved. Modern endpoint protection, application control, email filtering and restricted user permissions can all play a part. The right combination depends on your environment.
The key question is whether protection is active, current and managed consistently. If some devices report into one system and others are effectively unmanaged, that gap needs attention. Remote and hybrid working has made this more important, because not every device now sits neatly behind one office firewall.
Security update management
Unsupported software is a major issue under Cyber Essentials. Operating systems, applications and firmware must be supported by the vendor and updated in a timely way to address vulnerabilities.
This is often the hardest part for organisations with older systems or specialist software. You may have a line-of-business application that only runs on a legacy platform, or equipment that cannot easily be upgraded without operational disruption. That does not always make certification impossible, but it does mean you need to think carefully about scope, replacement plans or compensating arrangements.
A practical checklist should confirm which systems are supported, who is responsible for patching them, how quickly high-risk updates are applied and whether there are any exceptions. If there are exceptions, they should be documented and reviewed rather than quietly tolerated.
Common gaps that trip organisations up
Most failed or delayed applications do not happen because an organisation has ignored security altogether. They happen because one or two details were missed.
A device running an out-of-date operating system is a common example. So is an administrator account that has no extra protection, or remote access being enabled more widely than intended. Shared devices can create confusion too, especially if nobody is clear about who is responsible for their updates and security settings.
Cloud services deserve special mention. Many organisations assume Cyber Essentials is mainly about on-site equipment, but Microsoft 365 tenants, email systems and cloud-based administration tools often sit squarely within scope. If multi-factor authentication, admin controls and access settings are weak there, it can undermine the rest of your position.
How to use a Cyber Essentials requirements checklist properly
The most effective approach is to treat the checklist as a readiness review, not a formality. Start by identifying the people, devices, software and services that fall within scope. Then test each control area honestly against what is happening now, not what should be happening according to policy.
That means checking real device settings, real account permissions and real update status. It also means speaking to whoever manages your systems day to day, whether that is an internal team member or an external IT partner. Assumptions are where problems creep in.
If you find gaps, resolve the highest-risk issues first. Unsupported software, excessive admin access and exposed remote services generally deserve prompt attention. After that, focus on consistency. Cyber Essentials is built around secure basics applied properly across the organisation, not occasional good practice.
Why the checklist matters more for growing organisations
As organisations grow, their IT becomes less uniform. New starters join quickly, extra locations are added, remote working expands, and software choices multiply. Security controls that worked well for a ten-person office can become inconsistent across fifty users and several sites.
That is why a cyber essentials requirements checklist is especially useful during periods of change. It gives decision-makers a clearer picture of whether systems have stayed aligned with policy or quietly become fragmented. For schools and busy organisations with limited in-house IT capacity, that clarity is valuable.
It also helps with planning. If certification is part of a customer requirement, bid process or wider cyber security improvement plan, the checklist shows whether you are ready now or whether some remedial work is sensible first. Rushing into assessment before those issues are addressed rarely saves time.
When outside support makes sense
Some organisations can work through the checklist internally without much difficulty. Others benefit from a more structured review, particularly if their environment includes legacy systems, multiple sites, cloud platforms or a mixture of in-house and outsourced support.
External guidance can help separate genuine blockers from manageable issues. It can also make the process quicker by identifying scope correctly, checking technical settings and translating scheme requirements into practical actions. That is often where a provider such as Elmdale IT Services adds value – not by making the standard sound more complex than it is, but by helping organisations get the basics right with confidence.
Cyber Essentials works best when it reflects the way your organisation actually operates. A checklist is useful, but only if it leads to real improvements rather than a rushed pass on paper. If you approach it carefully, the certification process becomes less about satisfying a requirement and more about putting sound, defensible security foundations in place for the long term.