A password manager review should not begin with a list of popular apps or the lowest subscription price. For a business, school or established organisation, the real question is whether the service will reduce risk without creating another system that staff struggle to use.
Passwords remain a common route into business systems. Reused logins, passwords shared in spreadsheets, former employees retaining access and accounts without multi-factor authentication can all turn a simple oversight into a serious incident. A suitable password manager gives people a safer, more practical way to manage access – but only when it is selected, configured and supported properly.
Password Manager Review: What Matters Most
A consumer-focused password manager can be perfectly adequate for an individual. An organisation needs more control. The ability to create strong passwords is useful, but it is only one part of the decision.
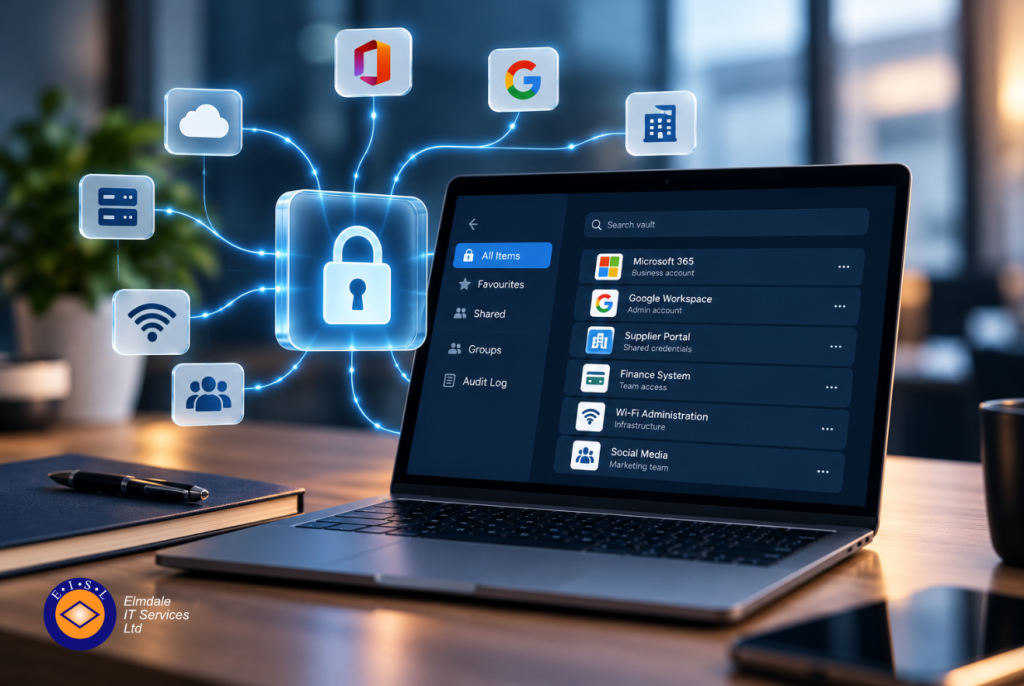
Start by considering where passwords are currently held and who needs access to them. Many organisations have shared credentials for supplier portals, social media accounts, cloud platforms, finance systems, Wi-Fi administration and critical infrastructure. These accounts must remain available to the right people while being protected from unnecessary exposure.
A good business password manager should make that possible through centrally managed vaults, groups and permissions. Staff should access only the credentials relevant to their role, while nominated administrators can oversee ownership and remove access quickly when someone changes jobs or leaves.
This is particularly valuable where IT responsibilities are shared between internal staff and an external support provider. The objective is not to hand over control of important accounts. It is to establish clear, accountable access that supports day-to-day work and continuity when an individual is unavailable.
Security must be matched by usable controls
Most reputable password managers use strong encryption. That is essential, but it should not end the review. Ask how the provider protects the vault, how encryption keys are handled and what security information is available for independent scrutiny.
Then focus on the controls that affect your organisation in practice. Multi-factor authentication should be available for every user, particularly administrators. It should support an authentication method that is realistic for your workforce, whether that is an authenticator app, security key or another approved option.
Look for controls over password sharing, clipboard use, offline access and exports. A vault that can be exported easily may be useful for contingency, but it also needs clear restrictions and monitoring. The right balance will depend on your risk profile. A small office may favour straightforward administration; a school or organisation handling sensitive data may require tighter controls and more detailed oversight.
Review Administration Before Features
A password manager often looks impressive in a demonstration because saving and filling passwords is simple. Administration is where the long-term value is decided.
Your chosen tool should work with the identity system you already use. For many organisations, this means connecting with Microsoft 365 or another central directory so users can be provisioned, managed and removed consistently. Single sign-on can improve the user experience, but it should be assessed carefully. If the identity platform is unavailable, consider how authorised users will access essential systems and whether an emergency process is in place.
Provisioning and offboarding deserve particular attention. When a new employee starts, can they receive access to the right shared vaults without being given broad permissions? When they leave, can their access be removed promptly, including access from personal devices and browser extensions? These questions are more valuable than a long features checklist.
Audit logs are equally important. Administrators should be able to see key events such as vault access, changes to permissions, sharing activity and failed sign-in attempts. Logs do not prevent every problem, but they help organisations investigate concerns, demonstrate good governance and identify gaps in their processes.
Shared accounts need clear ownership
Shared accounts are often the weakest point in password management. A team might all know the password for a supplier website, then change it informally when someone leaves. Before long, nobody is sure who owns the account, where recovery details are held or whether the password has been reused elsewhere.
A password manager can bring order to this, provided ownership is defined. Each important shared account should have a business owner, appropriate access groups and a documented recovery route. Recovery email addresses and telephone numbers should be controlled by the organisation rather than an individual wherever possible.
Do not overlook break-glass access. If a director, IT administrator or finance lead is unexpectedly unavailable, the organisation still needs a secure way to access critical services. This should be tightly controlled, limited to a small number of trusted people and reviewed regularly. It is an operational safeguard, not a convenience feature.
The Trade-Offs to Consider
There is no single best password manager for every organisation. A product that suits a ten-person business may not provide the controls required by a multi-site school or a growing organisation with formal compliance obligations.
Cost is one trade-off. Lower-priced plans can be appealing, but check whether they include central administration, user groups, reporting, emergency access, directory integration and responsive support. Adding these features later may change the total cost considerably.
Ease of use is another. If a system is difficult to use, staff may revert to saved browser passwords, personal vaults or informal sharing methods. A well-designed password manager should work across the browsers, computers and mobile devices your people actually use. Test it with representative users, including staff who are less confident with technology.
There is also a balance between convenience and control. Allowing personal devices and offline vault access can help remote workers, but it may increase exposure if a device is lost or unmanaged. Restricting every action can reduce risk, yet create delays that affect the business. Policies should reflect the information being protected and the way your teams operate.
For organisations subject to Cyber Essentials requirements or working towards stronger cyber security governance, the password manager should support wider controls rather than sit separately from them. It should complement multi-factor authentication, device management, leaver procedures, security awareness training and incident response planning.
A Practical Evaluation Process
Rather than choosing from a comparison table alone, assess a small number of suitable products against a written set of requirements. Involve the people who will administer the service, as well as users from departments that regularly manage shared accounts.
A sensible evaluation should cover security architecture, user management, integration with existing systems, auditing, emergency access, usability, data location where relevant, support arrangements and total cost. Ask suppliers how they handle security incidents, service outages and account recovery. The answers should be clear and specific, not limited to marketing language.
A short pilot can reveal issues that a demonstration will not. Test browser extensions, mobile access, password sharing, user invitations, account recovery and the offboarding process. Confirm that staff can use the tool without exposing passwords over email, messaging applications or paper notes.
It is also worth planning the migration before making a final commitment. Existing passwords may be scattered across browsers, spreadsheets, notebooks and old documents. Moving them into a managed vault is an opportunity to remove duplicates, reset weak or reused passwords and close accounts that are no longer needed. It should be handled carefully so critical services are not disrupted.
Adoption Is Part of Security
The strongest technical controls have limited value if people do not understand why the new process matters. Keep staff communication practical. Explain what is changing, how to get help and which habits need to stop, such as sharing passwords by email or retaining credentials after a role change.
Training should cover more than the browser extension. Users need to recognise suspicious sign-in prompts, protect their multi-factor authentication methods and report concerns promptly. Administrators need a clear procedure for handling access requests, recovery situations and suspected compromise.
For organisations without internal IT capacity, external guidance can make the process less disruptive. Elmdale IT Services can help assess password management alongside Microsoft 365, cyber security controls and the day-to-day support needs of your organisation.
The best choice is the one your people will use consistently, your administrators can manage confidently and your organisation can rely on when a key person is unavailable. Treat password management as a shared business process, not simply another application, and it becomes a practical layer of protection for everyday work.